Evidence that the controls exist, kept where it cannot be quietly changed
MCRC keeps a shipping company's resilience controls, incidents, drills and insurance obligations in one console. It covers every kind of event: cyber attacks, piracy and armed robbery, pollution, natural hazards and other disruptions to operations. Every entry is recorded in a tamper-evident log, so the company can show vetting inspectors, class, underwriters and its audit committee what was done and when.
Runs offline on your own computer · nothing leaves your office
Are the controls in place, and can I prove it?
One register for office and vessel controls, with evidence attached and dated.
Who must be told, and by when?
Notification clocks for flag, charterer, vetting and each insurance policy, started by the incident.
What do we disclose about risk and resilience?
A record that supports NIS2 obligations and SEC cybersecurity disclosure.
Controls & evidence
What the company says it does, and what it can show.
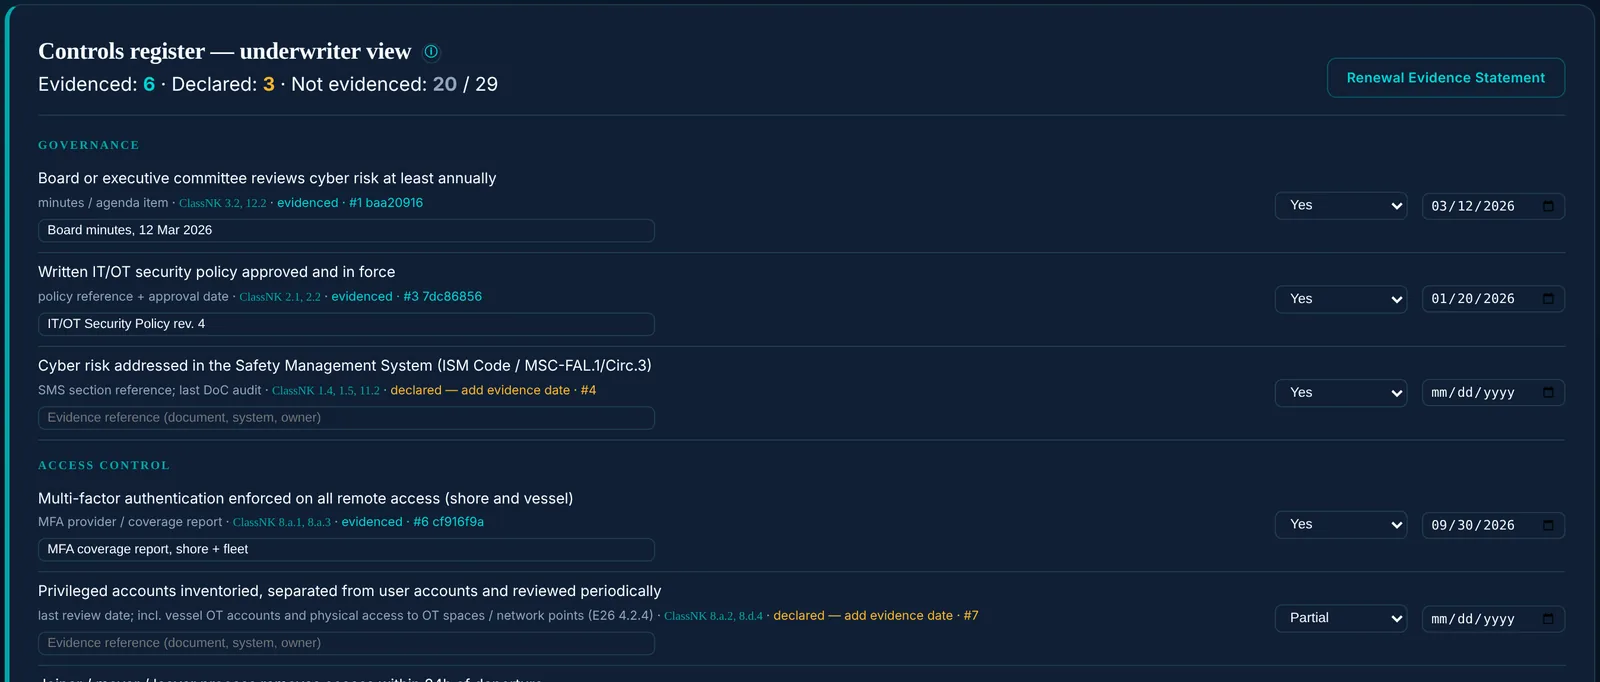
Controls registerWhich controls do underwriters and class expect?
Twenty-nine controls across office IT, vessel OT and cargo release, including the seven operation-phase controls of IACS UR E26. Each control carries its status, owner and evidence.
Renewal evidence statementWhat can we put in front of the underwriter?
Every control classed as evidenced, declared or not evidenced, exported for the insurance renewal.
DrillsDid the crew and office actually rehearse it?
Drill completion and the drill report recorded in the log.
Cargo release verificationWas the change of consignee confirmed?
Out-of-band verification of release and consignee changes. Delivery without the original bill of lading, against a letter of indemnity, is flagged.
Incidents & insurance
When something happens, the console shows who to notify and what the policy says.
Incident logWhat happened, and when did we know?
Incidents of every type, from a cyber attack to piracy, a pollution event or storm damage, recorded with their cause, the time of the event and the time it was recorded, kept separate.
Notification clocksWhose deadline runs first?
Presets for the Marshall Islands, Liberia, Panama, Bahamas, Cyprus and Malta flags, for vetting and for charterers.
Insurance programmeDoes this incident trigger the cyber exclusion?
One notification clock per policy. The incident cause sets the exclusion flag for the cyber attack clauses, and each notice is logged.
Cargo delivery recordWas cargo delivered on an unverified instruction?
Delivery events chained into the same log, with a warning when the instruction was not verified.
Tamper-evident log
The record that holds every other module together.
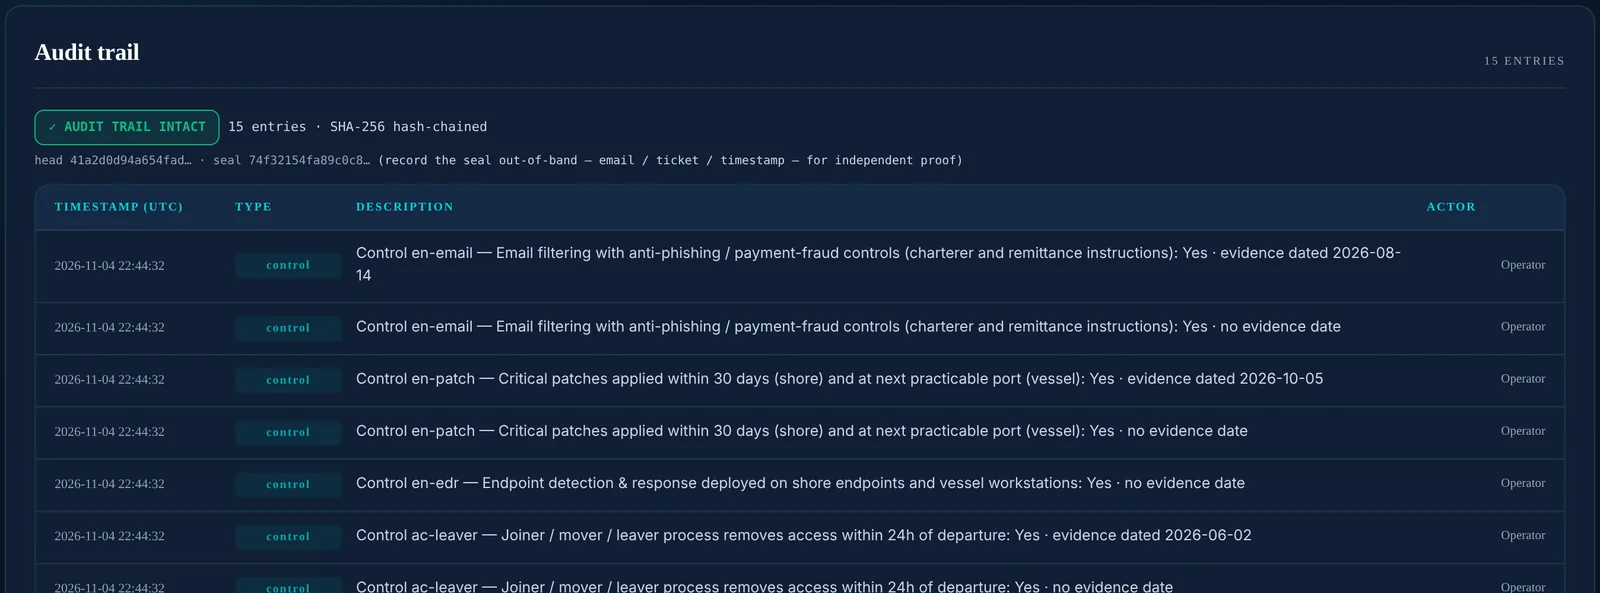
Each entry, from a control update to a policy notice, is linked to the one before it with a SHA-256 hash. Changing or removing any past entry breaks the chain, and the integrity check shows where.
What that does and does not prove: the chain shows that the log you are looking at is internally consistent and that no entry was altered without leaving a trace. It does not, by itself, stop someone with control of the whole file from rebuilding the entire history and its hashes. That is why every export and report prints the current chain head: lodge it with the auditor, class or a timestamping service, and the log can later be verified against a value nobody inside the company could change. Digital signatures and external anchoring are the step up to independent assurance; the single-file edition supports them by exposing the head, it does not perform them.
A single check that the chain is unbroken, run in the console.
A separate verifier that an auditor or underwriter can run on an exported log, without the console.
Scheme crosswalks
One set of evidence, mapped to every scheme that asks for it.
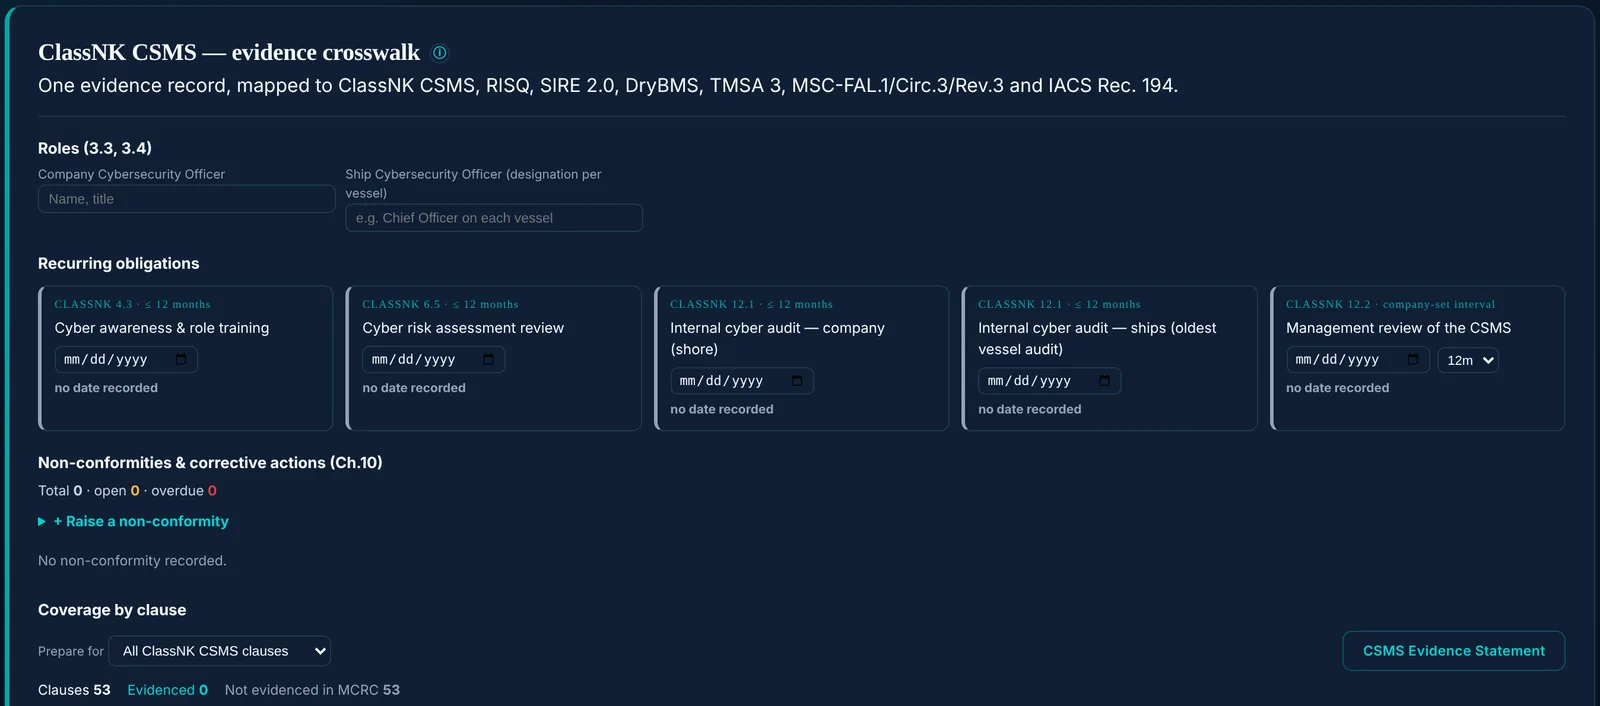
Class CSMS crosswalkWhich clauses does our evidence already cover?
Clause mapping from the ClassNK Guidelines for Cyber Security Management Systems for Ships to the other schemes, with a coverage view filtered by scheme.
Vetting & industry schemesWhat will the inspector ask?
RISQ, SIRE 2.0, DryBMS and TMSA 3 mapped to the same controls.
IMO & IACS guidanceIs cyber risk inside the safety management system?
MSC-FAL.1/Circ.3/Rev.3, IACS Recommendation 194 and the IACS cyber resilience requirements UR E26 and E27.
Renewal clocks & corrective actionsWhat expires, and what is still open?
Twelve-month review clocks and a register of non-conformities and corrective action plans.
What MCRC is, and what it is not
It is
A governance and evidence console. It records controls, incidents, notices and drills, and shows which obligations they meet.
It is not
A monitoring or intrusion-detection system, and not a claims register. The log is tamper-evident, not tamper-proof: it shows that a record was changed, and it cannot on its own prove who changed it or rule out a rebuilt history. Non-repudiation needs the chain head anchored outside the company and entries signed — a multi-user production deployment, not the single-file edition.